Smarter Network Security Software at Scale
Track every configuration change, run automated compliance checks, and scan for vulnerabilities in one place. rConfig helps you meet ISO, NIST, GDPR, HIPAA, and PCI-DSS requirements with workflows built for large, multi-vendor networks.
Why rConfig’s Network Security Auditing Tool Matters
rConfig strengthens network compliance for regulated environments, turning audit panic into process.
Ensure Full Traceability
Untracked changes create blind spots and audit gaps. rConfig logs every config change with who, what, when, and where for complete traceability.
Automate Compliance Checks
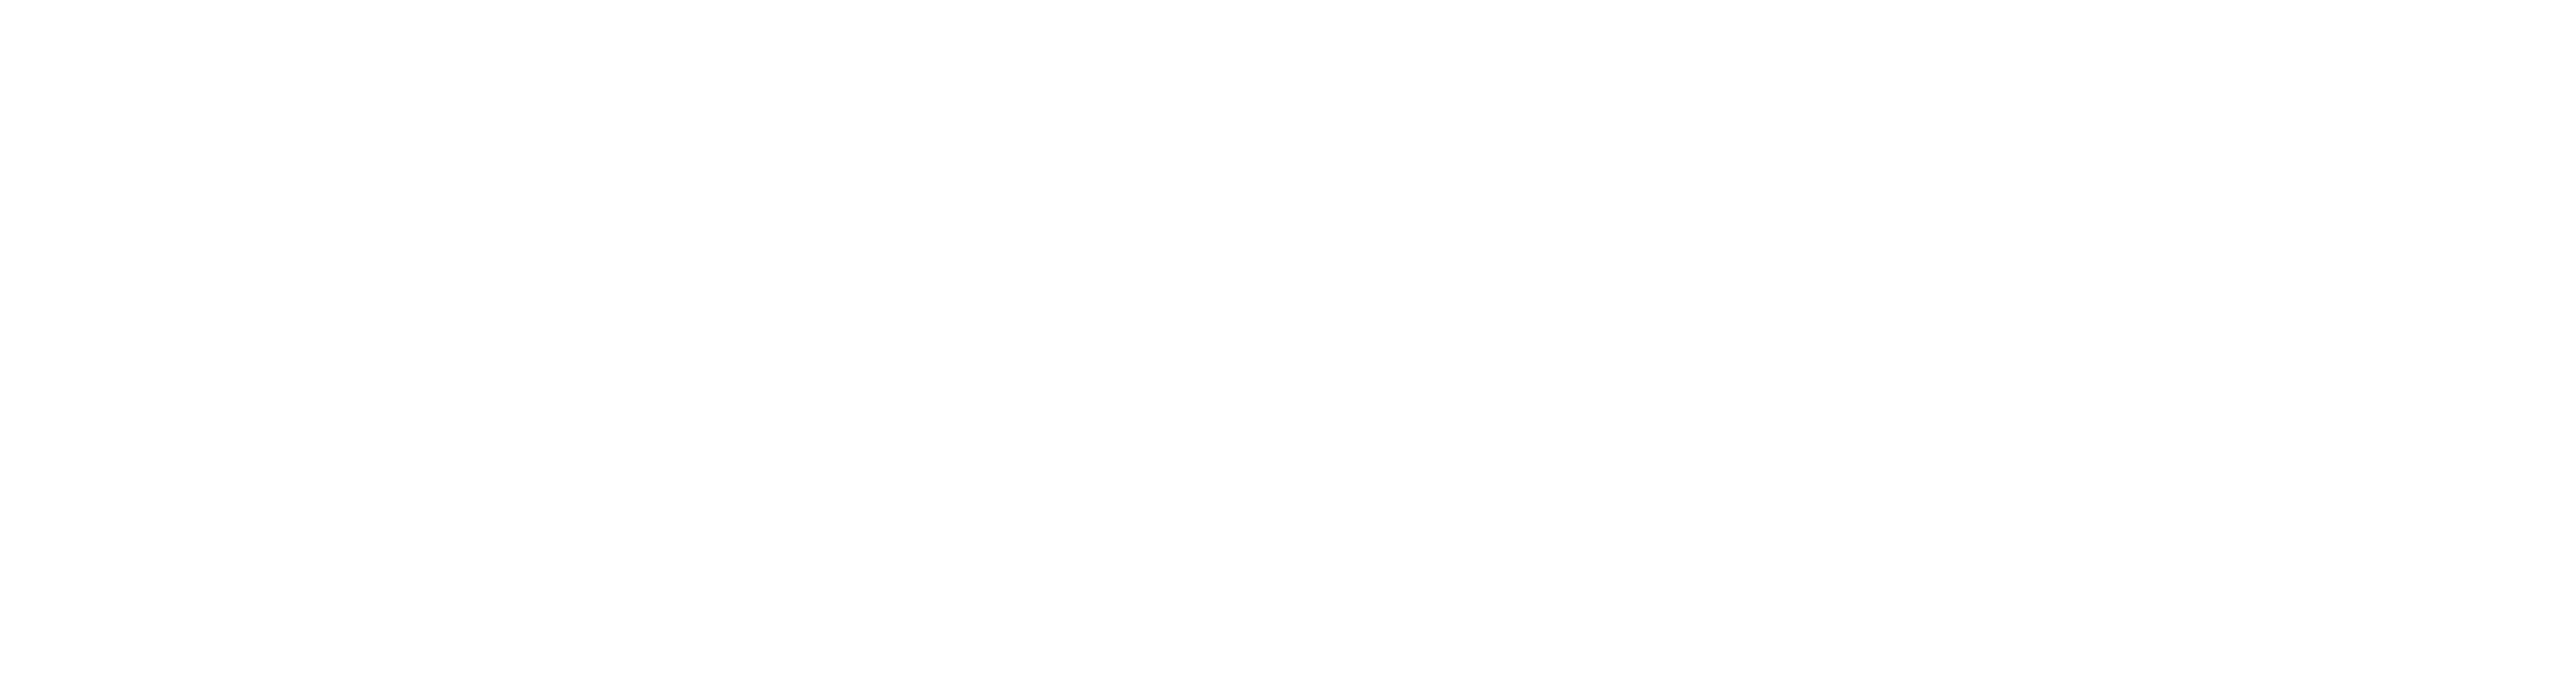
Validate configurations against ISO 27001, NIST, GDPR, HIPAA and internal policies using rule-driven checks, baselines and version control.
Prevent Configuration Drift
As a network configuration management software, rConfig uses templates and version tracking to keep configs aligned across sites and device types, shrinking your audit scope and preventing shadow IT.
Detect & Respond Instantly
Real-time alerts and CVE-aware insights flag risky changes and vulnerable devices, mapped to MITRE ATT&CK threat categories.
Explore Our Network Security Tool Capabilities
From real-time change detection to audit-ready reporting, rConfig gives you all the tools to track, verify, and secure your network.
Change Detection
Automatically detect and alert on unauthorised configuration changes across your network.
Audit Logging
Maintain tamper-proof audit records of every configuration change and user action.
Compliance Engine
Enforce policies automatically using rules mapped to the CIS Critical Security Controls.
Vulnerability Scan
Correlate device firmware with CVE intelligence to identify known security vulnerabilities.
rConfig’s Network Security Auditing Process
Detect Changes
Continuously monitor and flag unauthorised mods.
Capture Diff
Snapshot configs before & after to see exactly what changed.
Log Audit Trail
Record user, time and device in a tamper-proof log.
Report & Alert
Validate against policies and generate compliance reports.
Network Security Software for Every Environment
MSPs
Run recurring audits across distributed network operations with policy templates, version tagging and scheduled compliance reports. Learn about MSP features
Enterprises
Built for enterprises, rConfig enforces internal standards while deploying validated configurations across on-prem, data centre and cloud environments. Learn about Enterprise features
Regulated Industries
rConfig provides IT solutions for government, healthcare and finance, detecting drift and simplifying audits for HIPAA, PCI-DSS and the NIS2 Directive. Learn about Government Solutions
Frequently Asked Questions
What is network security software for enterprise IT environments?
Network security software helps protect enterprise networks by enforcing security policies, detecting risks and supporting compliance across network infrastructure. Solutions such as rConfig strengthen security by automating configuration management, detecting configuration drift and maintaining audit-ready records.
What are network security monitoring tools in enterprise networks?
Network security monitoring tools analyse network traffic, logs and device activity to detect threats, anomalies and operational issues in real time. They work alongside configuration auditing solutions to provide both operational visibility and continuous compliance.
How do I scan my network for vulnerabilities across enterprise infrastructure?
Enterprise organisations typically use dedicated vulnerability scanners to identify known CVEs, missing patches and exposed services. rConfig complements vulnerability scanning by correlating security intelligence with device configurations, helping teams prioritise remediation and validate secure network configurations.
What is a network vulnerability scanner for enterprise networks?
A network vulnerability scanner identifies known software vulnerabilities, outdated firmware and missing security patches across enterprise infrastructure. Combined with configuration management software, it provides the context needed to assess risk and maintain compliance.
How to audit network security in enterprise environments?
Network security is audited by collecting device configurations, comparing them against approved security baselines and identifying policy violations. Automated auditing simplifies compliance reporting, detects unauthorised changes and provides a complete audit trail.
What are the tools used in network security for enterprise networks?
Enterprise network security typically combines firewalls, SIEM platforms, vulnerability scanners, network security monitoring tools and configuration management software. Together, these technologies improve visibility, enforce security policies and support regulatory compliance across complex network environments.
What is network compliance monitoring?
Network compliance monitoring involves continuously tracking configuration changes, enforcing policies (like ISO 27001 or NIST) and auditing user activity to ensure network devices meet security and regulatory standards.
Can I track all changes in real time with rConfig?
Yes, rConfig's core engine detects changes as they happen, capturing snapshots before and after to visualise exact differences and alerting you to unauthorised modifications.
Which compliance frameworks does rConfig support?
rConfig allows you to build rule sets that align with major frameworks like ISO 27001, NIST, GDPR, HIPAA and PCI-DSS. You can customise these policies to match your specific internal governance requirements.
How does rConfig handle audit logging?
Every action, whether a configuration change, a login or a policy update, is recorded in a centralised, tamper-proof audit log. This provides the 'who, what, when' evidence needed for external audits.
Does rConfig detect security vulnerabilities?
Absolutely. By integrating with CVE databases, rConfig scans your device inventory (firmware versions and configs) to identify known vulnerabilities, helping you prioritise patching efforts.
Stay Compliant and Secure
Book a free demo or talk with our team to see how rConfig simplifies audits, tracks every change, and helps you meet your security objectives.