NIS2-Compliant Network Configuration Management
Meet NIS2 obligations with real-time configuration monitoring, secure backups, audit logging, and automated policy enforcement across every network device.
Why NIS2 Requires Strong Network Configuration Management
NIS2 significantly raises expectations for security baselines, change monitoring, incident detection, and operational resilience across the EU.
Security Controls
NIS2 requires organisations to implement “state-of-the-art” security measures. Configuration integrity is a core foundation.
Full Traceability
Untracked changes violate NIS2 expectations around audit trails. Maintain complete accountability for every device change.
Operational Risk
Misconfigurations and drift can lead to NIS2-reportable incidents. Reduce downtime by automating drift detection.
Incident Response
Enable rapid recovery after security failures with automated versioning, secure backups, and one-click restore workflows.
How rConfig Helps You Achieve NIS2 Network Compliance
From automated backups to detailed audit logs, our platform provides the technical controls necessary for EU regulatory adherence.
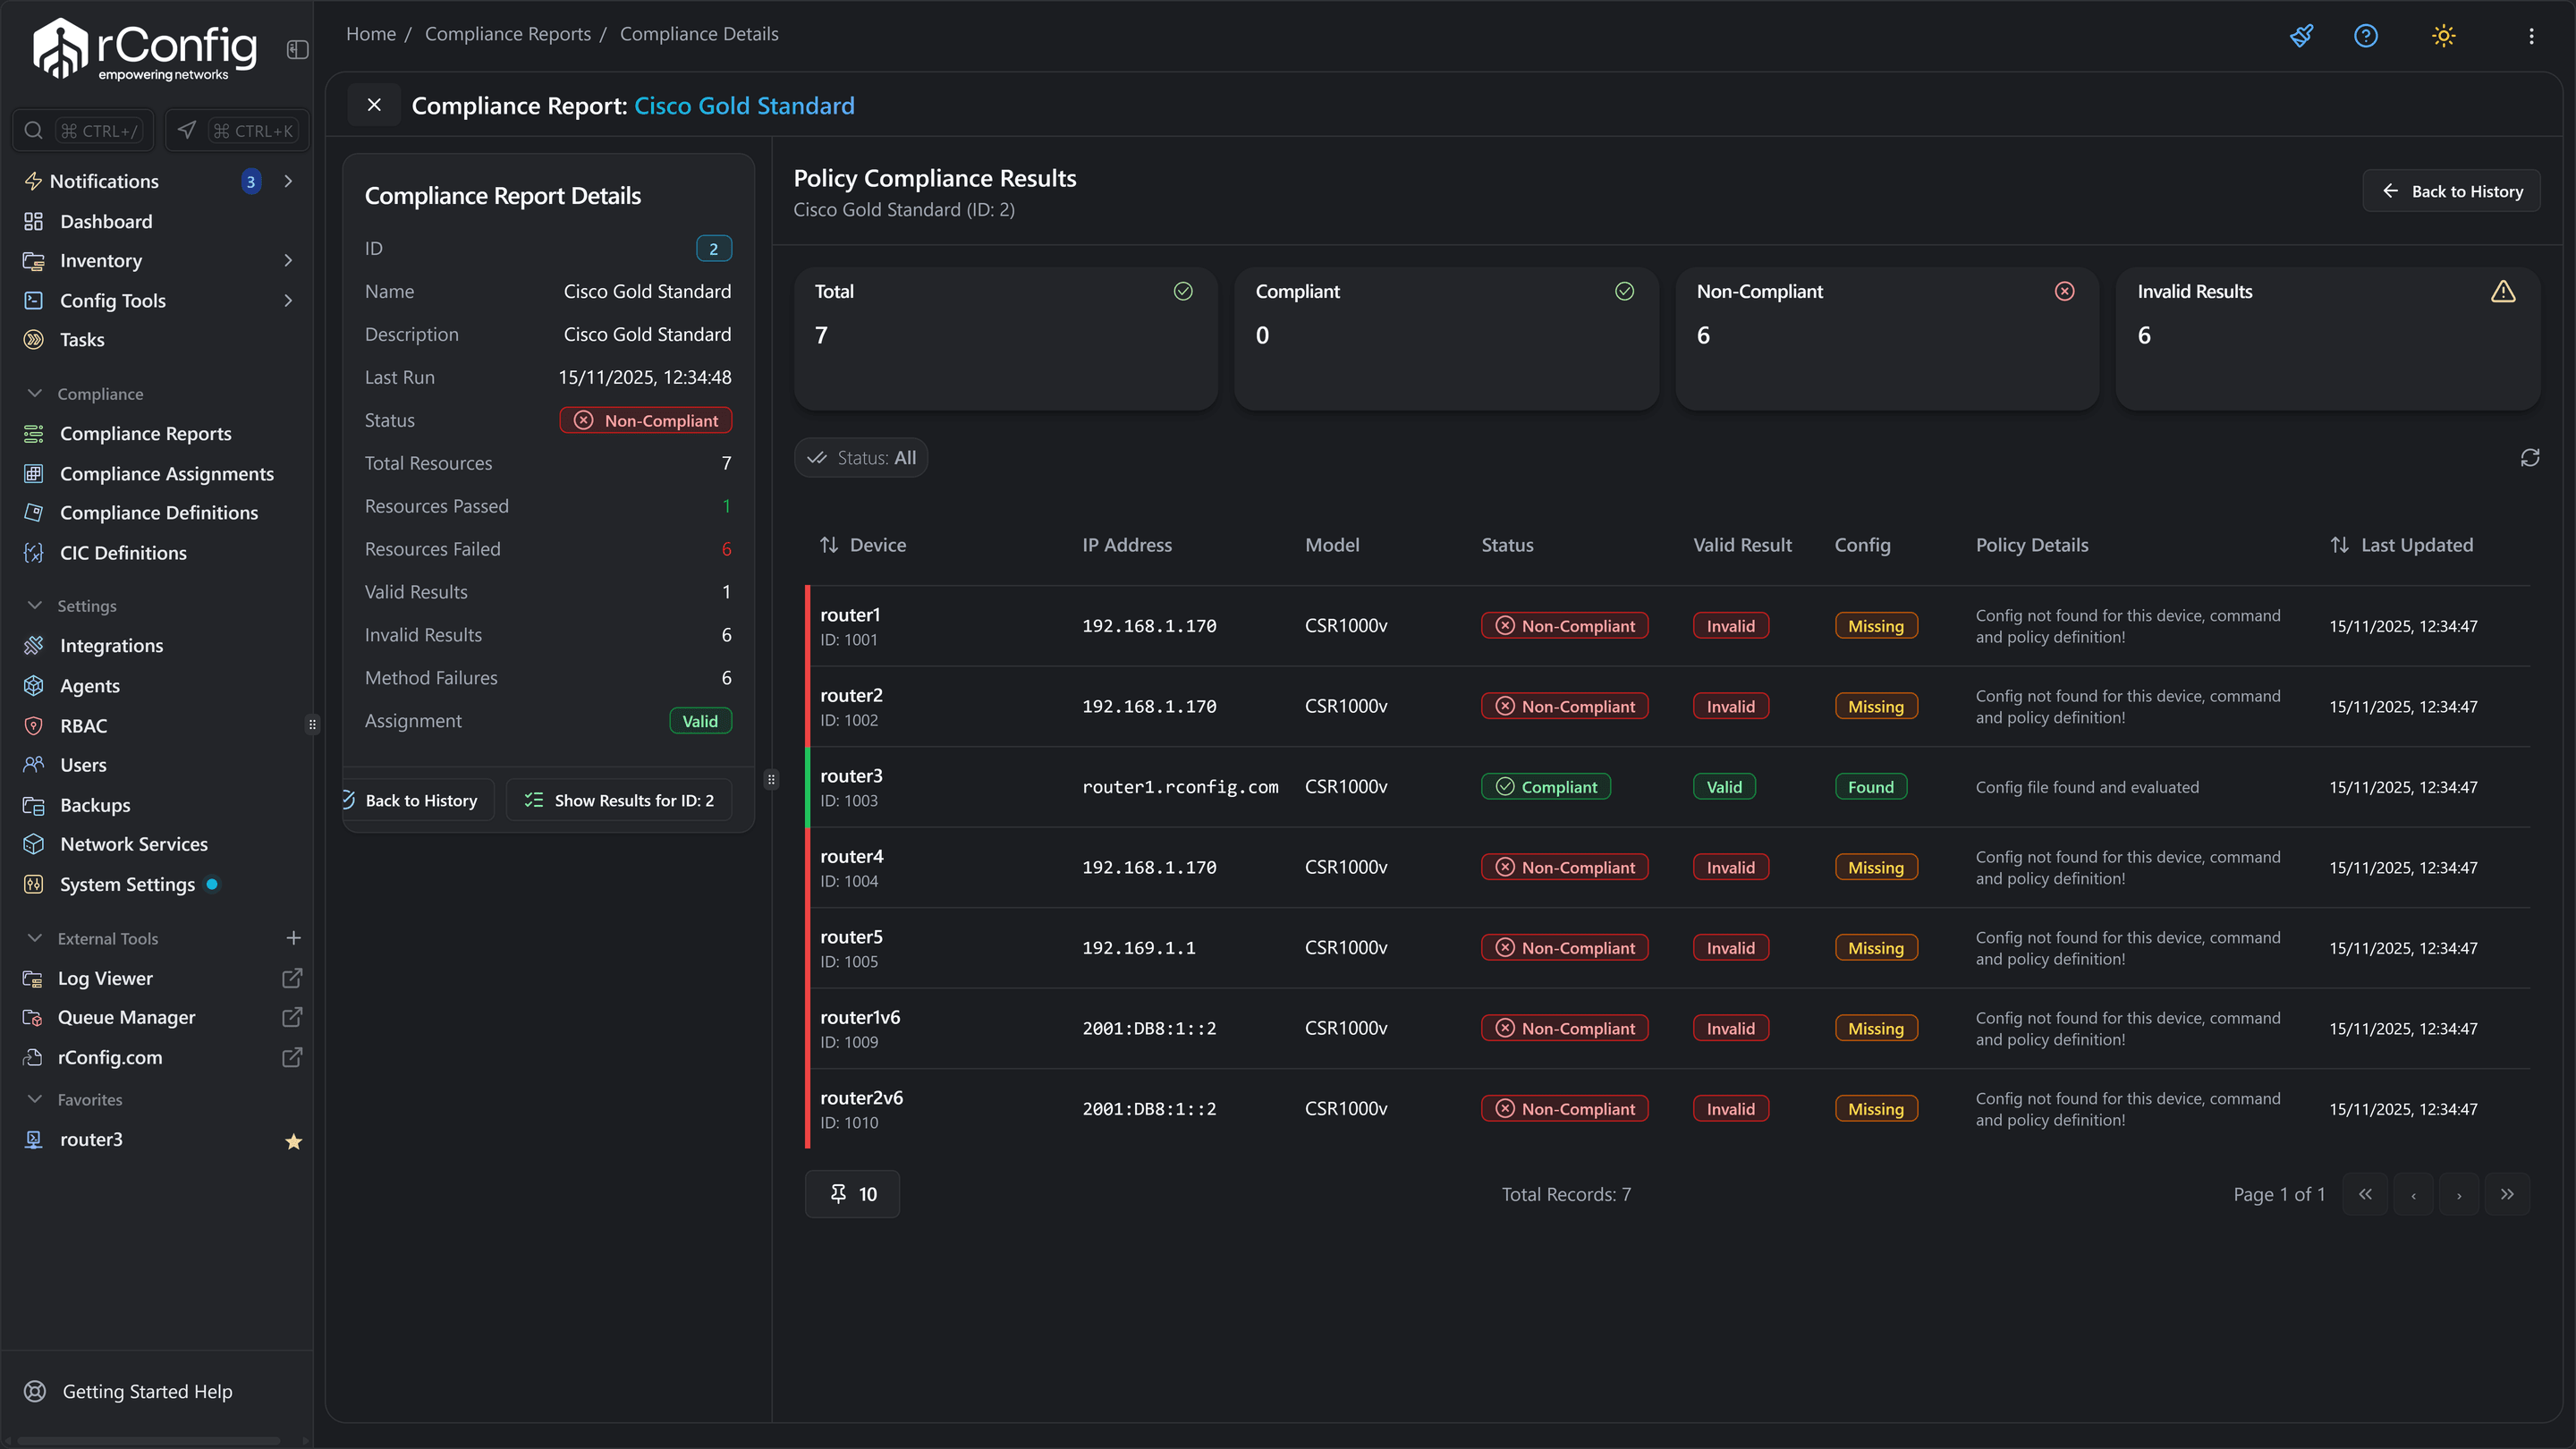
Real-Time Change Detection
Track every modification across your network with timestamped logs, user attribution, and before/after diffs, essential for NIS2 auditability.
Automated Backups & Version Control
Ensure all configs are securely stored, versioned, and recoverable, reducing the impact of outages and attacks as mandated by business continuity clauses.
Policy Enforcement & Drift Detection
Detect deviations from approved baselines instantly. Enforce configuration standards across multi-vendor environments to prevent vulnerabilities.
Secure Access & Audit Logging
Meet NIS2’s authentication, authorisation, and traceability requirements with tamper-proof logs, session recording, and RBAC.
Mapped to NIS2 Articles & Security Requirements
See exactly how rConfig supports your compliance journey.
- NIS2 RequirementRisk-Based Security ControlsHow rConfig Supports ItConfig integrity monitoring, version control, full audit history.
- NIS2 RequirementIncident HandlingHow rConfig Supports ItOne-click restore workflows, fast rollback, automated drift detection.
- NIS2 RequirementBusiness ContinuityHow rConfig Supports ItAutomated daily/hourly backups, off-box secure storage, redundancy.
- NIS2 RequirementSupply Chain SecurityHow rConfig Supports ItVendor-agnostic compliance visibility across the entire network stack.
- NIS2 RequirementLogging & Audit TrailsHow rConfig Supports ItFull device-level command accounting and change logging.
- NIS2 RequirementAccess Control (Zero Trust)How rConfig Supports ItRBAC, session history tracking, config access auditing.
- NIS2 RequirementVulnerability HandlingHow rConfig Supports ItFirmware version awareness, potential vulnerability matching.
| NIS2 Requirement | How rConfig Supports It |
|---|---|
| Risk-Based Security Controls | Config integrity monitoring, version control, full audit history. |
| Incident Handling | One-click restore workflows, fast rollback, automated drift detection. |
| Business Continuity | Automated daily/hourly backups, off-box secure storage, redundancy. |
| Supply Chain Security | Vendor-agnostic compliance visibility across the entire network stack. |
| Logging & Audit Trails | Full device-level command accounting and change logging. |
| Access Control (Zero Trust) | RBAC, session history tracking, config access auditing. |
| Vulnerability Handling | Firmware version awareness, potential vulnerability matching. |
How rConfig Helps You Stay Compliant, Step-by-Step
Discover Devices & Baseline
Identify your full network inventory and establish approved configuration baselines.
Monitor & Detect Changes
Automatically track unauthorised changes, policy violations, or configuration drift in real-time.
Enforce Policies
Apply compliance rules across devices and vendors to maintain security standards.
Generate Audit-Ready Reports
Export logs, baselines, diffs, and history for NIS2 assessments and external auditors.
NIS2 Compliance in Action
Critical Infrastructure Operators
Guarantee traceability, protect service availability, and meet regulatory expectations for energy, transport, and water sectors.
MSPs & Network Providers
Manage client networks with verifiable compliance and shared audit logs. Provide proof of service integrity easily.
Enterprise Security Teams
Strengthen governance, reduce risk of drift, and support incident response workflows with granular version control.
Frequently Asked Questions
What is NIS2 and why does configuration management matter?
NIS2 is the EU's updated directive on security of network and information systems. Configuration management is critical because NIS2 requires state-of-the-art security, risk analysis, and incident handling, all of which depend on knowing exactly how your network is configured and detecting unauthorized changes immediately.
How does rConfig help organisations meet NIS2 requirements?
rConfig automates the technical controls required by NIS2: configuration backups for business continuity, diff detection for incident analysis, and detailed audit logging for accountability and reporting.
Does NIS2 require configuration backups?
Yes, under Article 21 (Business Continuity), organizations must have backup management strategies. rConfig automates this process, ensuring you can restore network devices quickly in the event of an incident.
How does rConfig support NIS2 audit logging?
rConfig logs who accessed what device, what commands were run, and what configuration changes were made. This provides the granular audit trail required for regulatory assessments.
Can rConfig detect unauthorised changes for NIS2 incident handling?
Absolutely. rConfig runs scheduled and real-time checks. If a configuration drifts from its baseline or changes unexpectedly, alerts are triggered, allowing for immediate incident response.
Does NIS2 require multi-vendor visibility?
While NIS2 doesn't specify 'multi-vendor', it requires comprehensive security coverage. Since most critical infrastructure uses mixed vendors (Cisco, Juniper, HP, etc.), rConfig's vendor-agnostic approach ensures no compliance gaps exist in your network.
Be Ready for NIS2, Strengthen Your Network Configuration Management
Automate compliance, enforce policies, detect risks early, and keep your network audit-ready with rConfig.