rConfig Blog
Deep dives on network automation, compliance, security, and the future of configuration management.
Featured
 Network configuration management
Restorepoint Is Now Skylar Compliance: What It Means and Your NCM Options
If you went looking for Restorepoint recently and landed on a page titled Skylar Compliance, you are not lost. The product you knew has been renamed, folded into a larger suite, and repositioned. The configuration backup and recovery engine is still in there. But the name on the box, the surrounding pitch, and the buying motion around it have all changed.
 The Network Engineer's Case Against Autonomous AI
Why Network Engineers Still Don't Trust AI With the Network
We'll let AI write production code and draft legal contracts. Ask it to touch BGP on a core router and the room goes quiet. Here's why that instinct is correct.
 Enterprise Scale
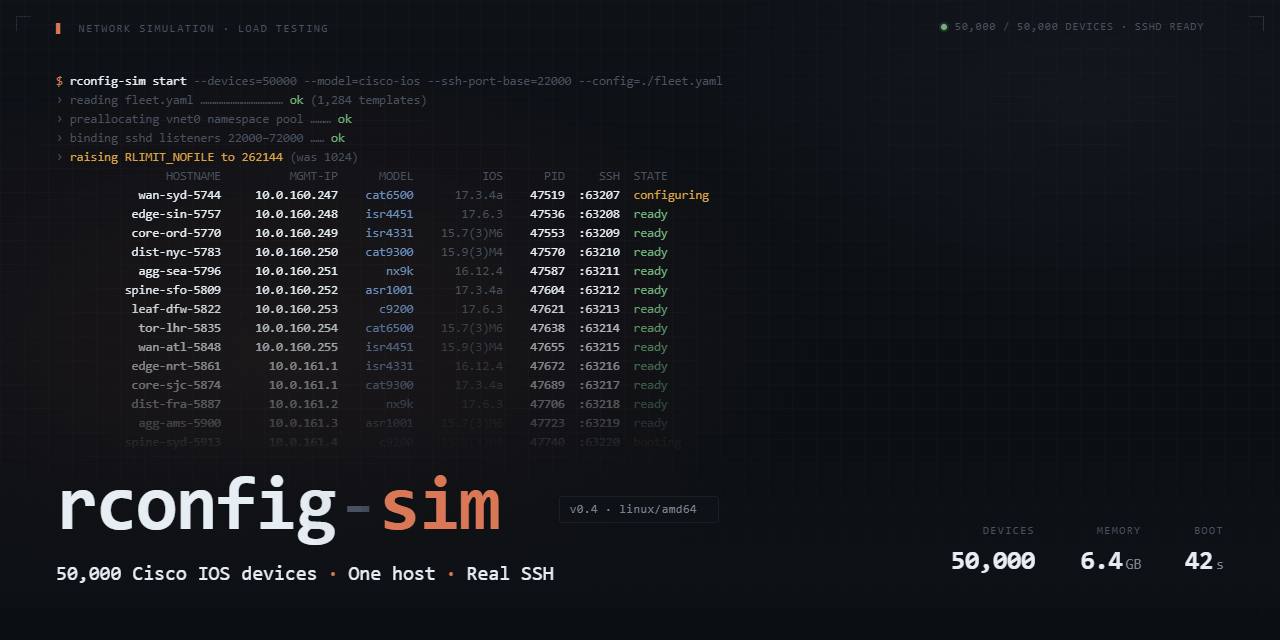
The NCM Industry Has an Evidence Problem. Ours Is 50,000 Devices in 21 Minutes.
The network config management industry quotes scale without evidence. rConfig pulled 50,000 devices in 21 minutes on one host. Open source test bed included.
 Rconfig vector
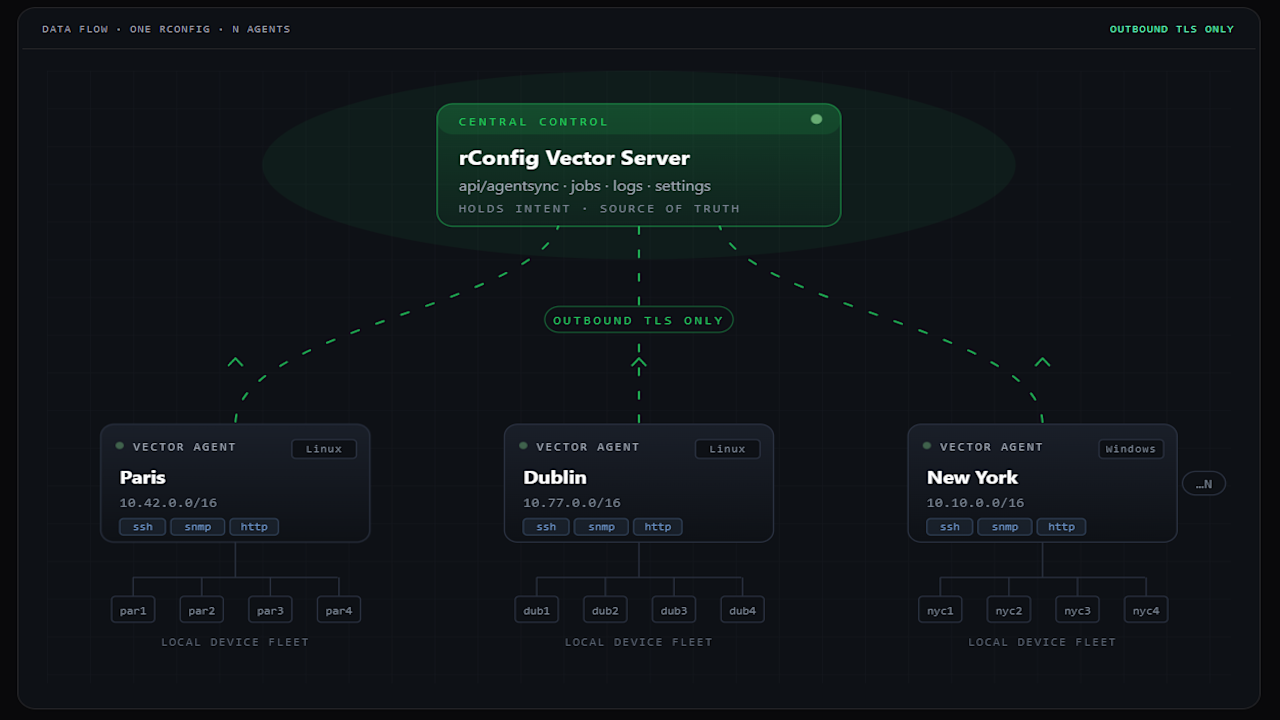
How an MSP Runs the rConfig Vector Suite End to End
<p> Network configuration management used to be a single-instance problem. One server, one rack of devices, one team that owned them. The job was backup, diff, rollback, and an annual compliance report. </p> <p> MSPs and large operators do not have that problem. They have a fleet of customers, each with their own kit, each in a different building, each with auditors who want to see their own access list and nobody else's. The old shape of NCM does not fit that work. You cannot expose the operator console to a customer. You cannot run one collector per customer site if every collector needs an inbound firewall hole. You cannot build a per-tenant brand on top of a tool that was designed for one company. </p>
 rConfig V8
rConfig v8.2.0: New Device Integrations, Custom Dashboards & a Live Debug Console
rConfig v8.2.0 is officially out, and honestly, this one has been a labour of love. It's a big release, packed with features we've been asked for, features we've wanted to ship for a while, and a handful of quality-of-life improvements that make day-to-day work in rConfig just nicer.
 Network Change Management
A CTOs Guide to Automated Network Configuration Auditing
Learn how automated configuration auditing ensures compliance, enforces policies, and provides verifiable evidence for network security.
 Network Change Management
Config Compare and Diff for Network Devices: Understanding Configuration Changes
t starts with a concept called a configuration diff. Think of it like the "track changes" feature in a word processor, but built specifically for the syntax and logic of network device configurations. A diff tool doesn't just tell you that a file was changed; it shows you precisely what was changed, line by line. It intelligently compares two versions of a configuration file—say, the current one and the one from yesterday—and presents a clear, visual summary of the differences.
 Network Change Management
Why A Network Config Audit Trail Is Not Optional
A configuration audit trail is the tangible output of maintaining a configuration history. Think of it as a complete historical ledger for your network devices. For every change, it must answer three simple but vital questions: who made the change, what exactly was changed, and when did it happen. This level of detail is what separates a true audit trail from a simple folder of backup files. Backups are static snapshots in time. They tell you what the configuration looked like on Tuesday, but they tell you nothing about the five changes that happened between Monday and Tuesday.
 Network Configuration Management
A CTOs Guide to Network Configuration Management Tools in 2026
Adopting modern network configuration management tools is not an operational upgrade. It is a foundational business requirement for guaranteeing uptime, enforcing security policies, and maintaining compliance in a hyper-connected world. By 2026, the idea of a traditional network perimeter has all but dissolved. Our infrastructures are a complex weave of on-premise data centers, multiple public clouds, countless IoT endpoints, and critical edge computing sites. In this environment, relying on manual configuration changes through CLI is no longer just inefficient, it's a direct threat to business continuity. We’ve all seen the post-mortems where a single typo brought down a critical service.